Helium Use Case

Can You Prove NIS2 Control This Week?

When the question comes from leadership, an auditor, or a customer, "we think so" is not enough. This story shows how Helium turns scattered compliance work into visible control, continuous evidence, and audit-ready confidence.

Prove control fastShow evidence instantlyRemove audit panic
Leadership team reviewing a compliance dashboard with audit readiness and evidence status

The short version

From weak proof to visible control

Helium gives security leaders, operations teams, and auditors one shared view of posture, ownership, and improvement without relying on last-minute evidence collection.

01

Pressure builds fast

A growing Azure estate, rising audit pressure, and fragmented evidence made it hard to prove control when leadership needed answers.

02

Helium changes the model

Instead of chasing evidence before every review, the organization moved to one visible flow for findings, ownership, remediation, and proof.

03

Confidence replaces scramble

Audit prep stopped being a fire drill because the evidence trail was already built into daily operations.

The Story

What happens when compliance has to stand up to real pressure

This is not a story about checking boxes. It is a story about being able to answer hard questions quickly, show progress clearly, and prove that control exists beyond a PowerPoint.

Step 1

Fragmented compliance work across documents, dashboards, and disconnected tools

The Situation

The organization had serious security intent but no reliable way to prove it. Evidence lived across tools, decisions stayed in inboxes and meetings, and audit readiness depended on last-minute effort.

Leadership needed proof of control on demand, not another promise that the team would pull everything together before the next review.

Where They Got Stuck

  • Manual evidence collection with no single source of truth
  • Gaps fixed in practice but not tracked as auditable history
  • Managers unable to show improvement trends clearly
  • Audit prep treated as a project, not a daily operating model

Step 2

Customer Voice: Before and After Helium

Real excerpts from a customer team that uses Helium in daily Azure operations.

Before and after view of compliance operations moving from fragmented work to visible improvement

Before Helium

Challenge: High Azure complexity across development, test, and production environments created more exposure than the team could track manually.

Reality: Best-practice checks and configuration reviews were slow, expensive, and difficult to sustain at the level the business expected.

"Without the right tooling, continuous security governance became resource-intensive and risked competing priorities."
After Helium

Helium Action: A baseline health check created clear visibility in days and gave the team concrete remediation priorities instead of vague concerns.

Outcome: Continuous monitoring became part of daily engineering work, turning compliance from a periodic burden into an operational advantage.

"Helium quickly moved from assessment tool to an integrated support system for developers and managers."

Step 3

The Helium Approach

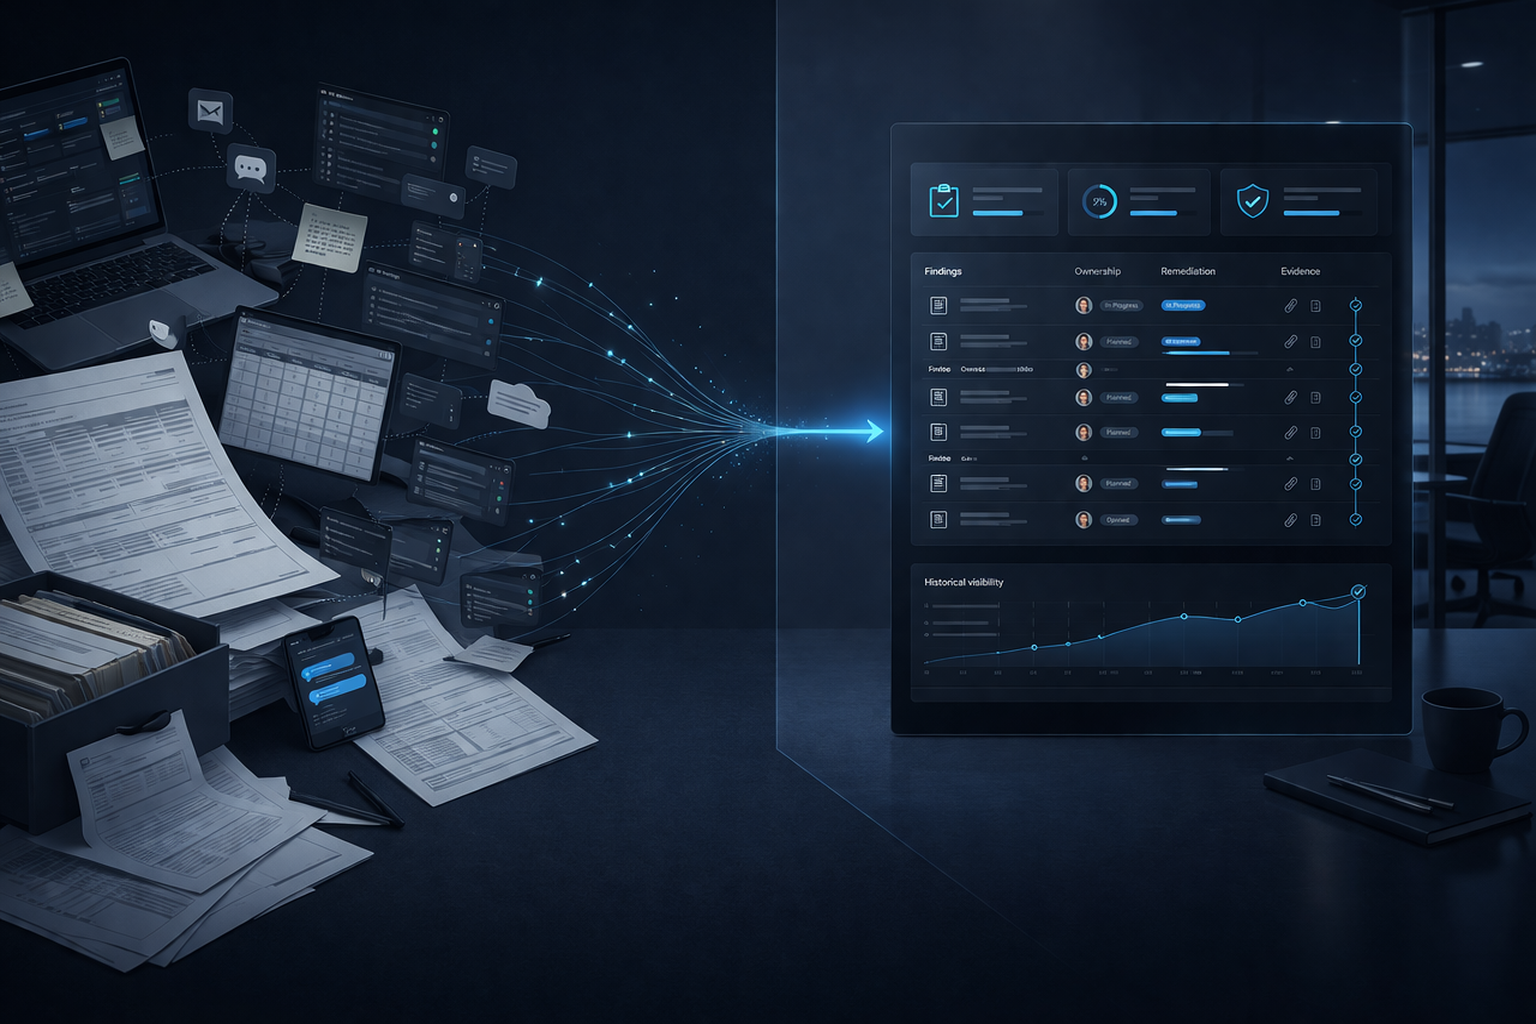
Helium established a single compliance narrative: current posture, identified gaps, clear ownership, and recorded improvement over time. Instead of rebuilding the same proof before every audit, the organization could show control continuously.

Visibility

One view of risk and compliance across identity, network, data, monitoring, and resilience.

History

Every finding and remediation is timestamped and retained as evidence.

Accountability

Teams can show who fixed what, how quickly, and the resulting compliance impact.

Transformation from scattered compliance inputs to one unified workflow with evidence and ownership

Step 4

Technical Testimonial

The customer highlighted Helium as a strategic security enabler: weekly review cycles, real-time production notifications, and measurable progress through level-based reporting.

"In production, real-time notifications are a central capability. When something deviates, we receive immediate information and can quickly correct both operational and security-related issues."

"A highly appreciated feature is the ability to create improvement actions directly in our Kanban board with one click, making the process smooth and integrated into our way of working."

Business Impact

  • Earlier fixes in development reduce expensive late corrections.
  • Production monitoring reduces stress and shortens time-to-remediation.
  • Clear visual risk prioritization helps teams focus on the right actions.
  • Unused components are identified when integrations are retired, reducing cost and risk.
  • Managers can prove both control and continuous improvement during audits.

Step 5

Capability-to-Control Mapping

Helium CapabilityNIS2 AreaHow Helium Supports
Identity & Access ControlAccess controlEnforces Entra ID and detects weak authorization before they become audit findings.
Example: A contractor account is granted excessive rights. Helium flags the issue and the team corrects access in hours, not weeks.
Network SecurityNetwork securityDetects public exposure, missing segmentation, and risky network paths.
Example: A sensitive service is exposed to the internet after a deployment change. Helium identifies the exposure immediately.
Encryption & Data ProtectionCryptographyValidates TLS, HTTPS, and key management policies continuously.
Example: A service falls back to weaker transport settings. Helium highlights the drift and provides remediation guidance.
Monitoring & LoggingIncident detectionEnsures logging, alerts, and monitoring coverage are complete and actionable.
Example: A critical workload lacks alert routing. Helium reports the gap before an incident reveals it.
Resilience & BackupBusiness continuityValidates backup, restore, and availability readiness.
Example: Restore testing fails for one key system. Helium captures the failure and tracks the fix to closure.

Conclusions

What the reader should walk away with

NIS2 confidence does not come from working harder a few weeks before an audit. It comes from an operating model where control, ownership, and evidence are visible every day.

Executive team reviewing outcome dashboard with compliance improvement and evidence history

The Outcome

Within one reporting cycle, the organization replaced reactive audit preparation with a repeatable operating model. Helium did not just identify risks; it created visible proof of improvement that executives, customers, and auditors could trust.

  • Live visibility into compliance posture across core NIS2 domains
  • Historical evidence showing what changed, by whom, and when
  • Executive confidence through transparent progress and ownership
  • A stronger customer and audit position built on visible control

“With Helium, we are ahead of other teams. Audits are no longer stressful because we can show both control and improvement history in minutes.”

IT Manager, Helium Customer

Call to Action

Why Helium

Helium combines three advantages that generic tools rarely deliver together: clear visibility, durable history, and proof of continuous improvement. For leaders, that means one thing: you can answer the control question with evidence, not reassurance.

If your goal is not just to work toward compliance, but to prove it at any time, Helium is built for exactly that.

How Helium Delivers This in Practice

Helium provides a continuous evidence trail across your Azure environment, turning governance into a repeatable operating model instead of a one-time compliance event.

Next Step

Book a 30-minute NIS2 readiness walkthrough. You will leave with a clear posture snapshot, your highest-priority risks, and the fastest path to stronger proof.

Security advisor leading a NIS2 readiness walkthrough with governance and evidence dashboard